Advisory and governance
180 days to an audit you can actually pass
A risk-based readiness programme that ends in a decision rather than a hope — and a vCISO engagement that keeps the compliance standing up afterwards.
The deadline is yours. This is the short one.
Organizations that missed the first round of NIS2 audits usually get 180 days, not a year — which is enough time to be ready and not enough to be leisurely about it. If your date is further out, the same programme stretches; the order of the work does not change.
Five things that are different at the end
Scope
Today
Unclear whether NIS2 applies, and to which systems
After 180 days
Approved scope and system boundaries, signed off by management
Policies and registers
Today
Incomplete, inconsistent, or written for a different framework
After 180 days
Approved and implemented policies, with asset, data and supplier registers that are current
Evidence
Today
Scattered across inboxes, drives and people’s memories
After 180 days
An organized evidence store and a compliance matrix an auditor can be walked through
Incident response, BCP and DRP
Today
Documented at best, never tested
After 180 days
Tested and documented, with the test itself as evidence
Readiness
Today
Nobody can say whether you would pass
After 180 days
Mock-audited, with a GO/NO-GO decision that has reasons behind it
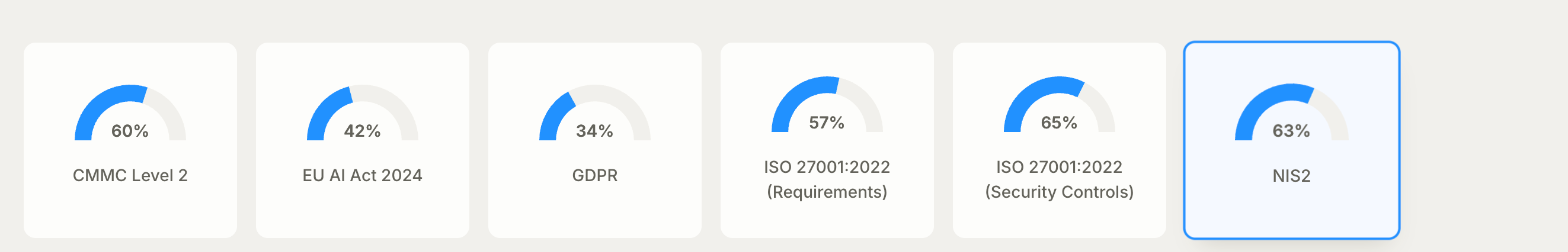
Three phases, ten steps
The sequence is the method. Scope before gap analysis, gap analysis before planning, and evidence collected as the work happens rather than assembled in the last fortnight.
- 01
Days 1–30
Scope and assess
Days 1 to 30. Establish whether and how NIS2 applies, fix the audit scope and system boundaries, review the asset, data and supplier registers, and run an accelerated gap analysis and risk assessment.
Gate Scope and system boundaries approved
- 02
Days 30–140
Build and fix
Days 30 to 140. Policies, procedures and registers written or brought up to date; access control, MFA, endpoint, logging, vulnerability management, backup and recovery reviewed and corrected; incident response, BCP and DRP built and tested; critical suppliers and outsourced ICT assessed.
Gate Controls corrected, continuity tested
- 03
Days 140–180
Prove and decide
Days 140 to 180. Evidence organized into something that can be presented, an internal mock audit run, corrective and preventive actions planned against what it finds, management and staff prepared for audit interviews, and a GO/NO-GO put to the leadership.
Gate Mock audit, then the GO/NO-GO decision
What happens, and when
Scope is a milestone with a date on it, not an assumption. Everything downstream depends on it, so it is decided by day 30 with management approval — the single most common reason these programmes run late.
- 01
Kick-off and scope
NIS2 applicability confirmed, audit scope and the boundaries of the in-scope systems defined and approved.
- 02
Gap analysis and risk assessment
An accelerated review against the requirements you are actually held to, with the risks that matter named rather than scored generically.
- 03
Prioritization and the 180-day plan
Findings ranked by risk, urgency and what is genuinely achievable in the time, then sequenced into a plan with owners and dates.
- 04
Policies, procedures, registers
Written or updated: the documents an auditor asks for first, and the asset, data and supplier registers behind them.
- 05
Technical controls
Access management, MFA, endpoint protection, logging, vulnerability management, backup and recovery — reviewed against the requirement and corrected where they fall short.
- 06
Incident response, BCP and DRP
Processes built where they are missing, and tested where they exist. An untested plan is not evidence of anything.
- 07
Supplier and ICT risk
Critical subcontractors and outsourced ICT services assessed, with the results on a heat map rather than in a spreadsheet nobody opens.
- 08
Evidence and the mock audit
The evidence an auditor will ask for, organized and indexed — then an internal audit run against it as if it were the real one.
- 09
Interview preparation and GO/NO-GO
Management and the staff who will be interviewed prepared for what is actually asked, and a GO/NO-GO assessment put to leadership before the official audit.
- 10
Corrective actions and monthly reporting
A CAPA plan for what the mock audit found, and the reporting rhythm that carries into the operational phase.
We will tell you not to go
The programme ends with a mock audit and a GO/NO-GO recommendation, and the recommendation is sometimes no. Postponing an audit is inconvenient. Failing one is a finding on the record, a remediation deadline set by somebody else, and a second audit you pay for anyway.
That is only worth anything if the mock audit is run the way the real one will be, so it follows the official audit’s own method: document review, sampled evidence, interviews, and technical controls demonstrated rather than described. Audit-critical controls are covered in full; the rest is sampled.
A GO comes with the reasons it is a GO — which is what management needs in order to sign it, and what turns out to be useful again the next time.
Prove and decide
GO
Evidence in place, the mock audit passed, and the reasons written down — which is what management needs in order to sign it.
NO-GO
Named gaps, what each one takes to close, and a realistic new date. Inconvenient, and cheaper than a finding on the record.
Three things, and the risks if they slip
These programmes rarely fail on the security work. They fail on decision latency, on internal capacity, and on scope that stays vague too long — so all three are planned for rather than discovered.
Decisions, on the dates they are needed
Scope approval by day 30 is a milestone, not a formality. Late scope pushes the gap analysis, and the gap analysis pushes everything.
IT capacity for the fixes
We can specify and verify a control; somebody has to implement it. Where capacity is short we say which audit-critical controls are at risk and what can defensibly wait for the longer plan.
Access to people and evidence
Interviews, walkthroughs, and the documents that already exist. Most organizations have more evidence than they think and less of it findable than they hope.
The part that decides whether it lasts
Passing an audit is a moment. Staying compliant is a job, and it is the job the readiness programme was building toward — which is why this runs inside a vCISO engagement rather than as a project that ends when the auditor leaves.
The preparation months carry a higher fixed fee than the operational months that follow. We keep the CISO and the information security officer roles, the authority contact, the reporting rhythm and the platform, and the registers stay current because somebody owns them.
Without that, the next audit starts from where this one started: evidence scattered, registers stale, and nobody able to say whether you would pass.
Frequently asked questions
The questions we hear most often from security and IT leaders.
Something not covered here? Ask us directly
At kick-off, not at signature — and the two are days apart rather than weeks. Platform access and onboarding, the kick-off itself and the naming of the information security officer to the supervisory authority all fall inside the first fortnight, and scope clarification and the gap analysis begin inside the first ten days.
The platform is part of the service on every engagement and included in the fee. Its hosting region is chosen before it is initialised — EU or US — so that is a decision taken with you at the start rather than something found out later.
A team rather than one person, so the programme does not pause when somebody is away: a lead vCISO who owns the professional side and the management reporting, a security officer expert who holds the statutory qualification and the authority contact, a consultant for policies, registers and evidence, and a technical expert for access, endpoint, logging, backup and recovery. Between them they hold ISO/IEC 27001 Lead Auditor, NIS2 auditor, ISO/IEC 42001 Lead Auditor, CISA and CISM. Roughly a fifth of the work is on site, weighted towards the assessment and the mock audit.
It can be an external mandatee where the applicable implementation allows one, and in our markets it does. We take the role with a named individual who meets the statutory education and qualification requirements and who is notified to the supervisory authority, and that person carries a documented minimum on-site presence. One thing to be plain about: your organisation’s head keeps the statutory liability. We perform the professional tasks and prepare the decisions — we cannot take the liability off anybody.
Two to three hours a month from the executive sponsor, for scope and plan approval, the monthly report and the GO/NO-GO. Three to four hours a week from whoever owns the project internally, usually the IT director. And one to one and a half days a week from IT operations through the first five months, because somebody has to implement and demonstrate the controls. That last figure is the real cost of a readiness programme, and you should know it before signing rather than discover it in month two.
Then some of it is not attempted, as a decision rather than a drift. Every finding is scored by risk, urgency and what is genuinely achievable in the time, into three groups: audit-critical and achievable now; audit-critical but longer — started immediately with a compensating control and evidence of progress on file; and not audit-critical, which moves into a separate longer-term plan and is deliberately kept out of the 180 days. We propose the split and your management approves it, at the sixty-day milestone.
Because the mock audit is run the way the real one will be rather than as a self-assessment. It follows the official audit’s own method — document review, sampled evidence, interviews, and technical controls demonstrated rather than described. Audit-critical controls are covered in full and the rest is sampled, and you receive the findings graded by severity with a corrective and preventive action plan against each. Where the evidence does not hold up, the recommendation is NO-GO.
No, and that separation is structural rather than a promise: the cybersecurity audit is performed by a registered independent auditor, and their fee is not part of ours. What we hold is the preparation, and then the coordination of the official audit itself in the CISO and information security officer roles.
A fixed monthly fee in two stages: higher through the preparation months, lower through the operational months that follow, with no hourly billing and the platform included. What moves the number is the size of the estate rather than the hours spent on it — how many people and user accounts, how many sites, how many systems fall inside the audit scope and at what security classification, and how many critical suppliers have to be assessed.
Is there a date in the calendar?
Tell us when the audit is and what has been done so far. The first useful output is a scope and a gap analysis, and both come early.