Skip to content

About us

The people behind Spirity

Good work starts with good people. Our team combines deep professional expertise with curiosity, collaboration, and a genuinely human approach.

Leadership

Meet the team

Whether we are solving a complex security challenge or sitting around the same table, we believe the strongest results come from trust and working together.

  • Portrait of Eva Szunomar

    Eva Szunomar

    Founder & CEO

    Experienced Head of Information Technology with a proven track record in the telecommunications industry. A skilled leader in transformational programmes, she specializes in building strong organizations to ensure seamless execution. As founder and CEO of Spirity, Eva also heads the Professional Services department, overseeing the IT aspects of mergers and acquisitions.

  • Portrait of Andras Lanyi

    Andras Lanyi

    VP of Sales & Marketing

    Extensive experience from a distinguished career in the insurance and financial industries, with decades of expertise in strategic leadership, project finance and risk management. He leads sales and marketing at Spirity, combining deep industry knowledge with a results-driven approach to building client relationships, and also heads the business in Austria.

  • Portrait of Balazs Csendes

    Balazs Csendes

    VP of Product & Strategy

    Seasoned IT and cybersecurity professional with over two decades of international experience. Formerly Sales Director for Central Eastern Europe, the Middle East and Africa at BlueVoyant, and Security Operations & Response Leader at IBM. Focused on shaping strategies that fortify organizations against cyber threats and ensure long-term resilience.

How we work

Expertise, and the willingness to sit with the problem

Cybersecurity advice is easy to give and hard to make useful. What separates the two is understanding the business you are advising — its constraints, its regulator, its appetite for change.

So we spend the time. Our engagements start with listening, and the roadmaps we produce are the ones your team can actually execute, not the ones that look most impressive in a slide deck.

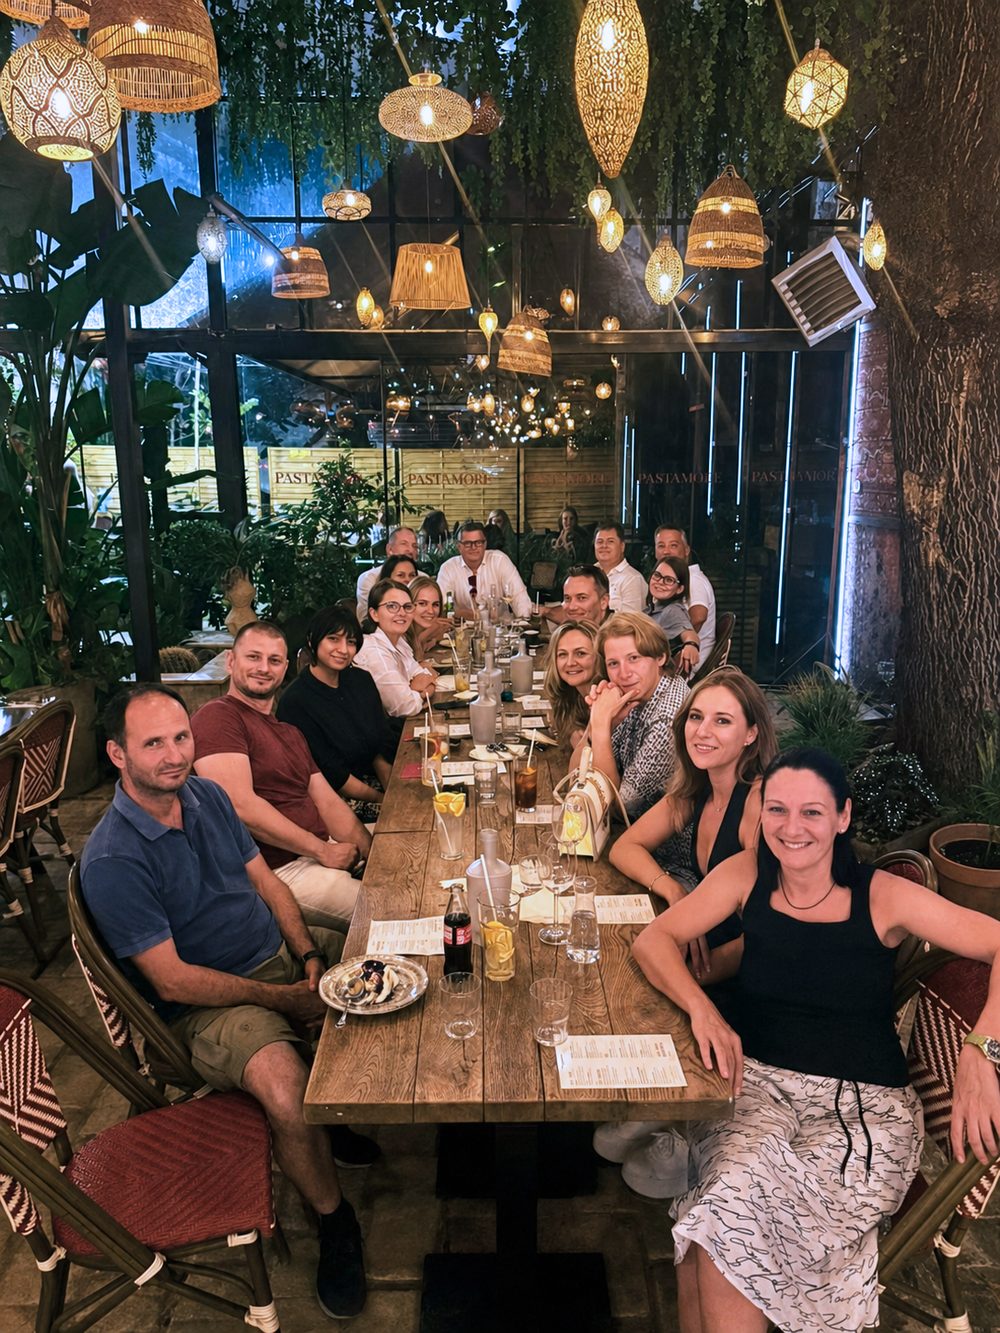
The Spirity team together at a long table during a company dinner
Global presence

Three offices, local expertise

Serving clients across multiple continents, with people on the ground in each region we operate in.

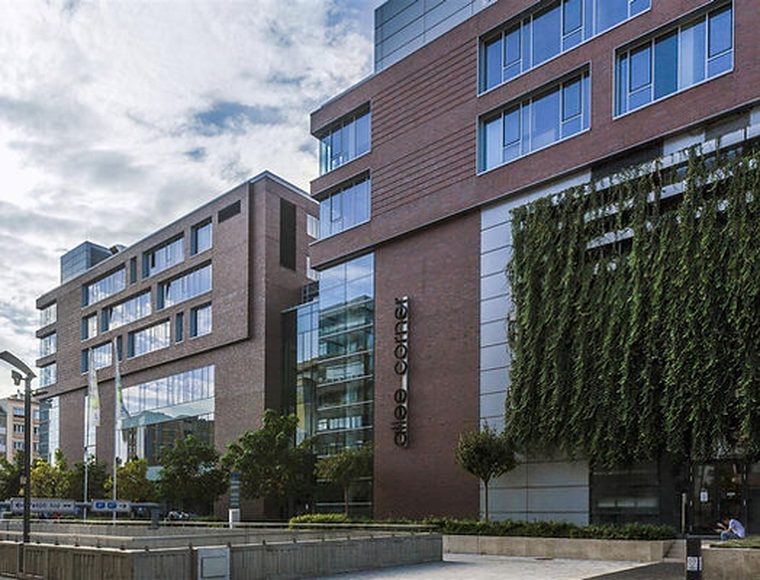
  • The Spirity office in Budapest

    Budapest

    Headquarters
    Október huszonharmadika utca 8-10.Budapest, 1117Hungary
    hello@spirity.hu
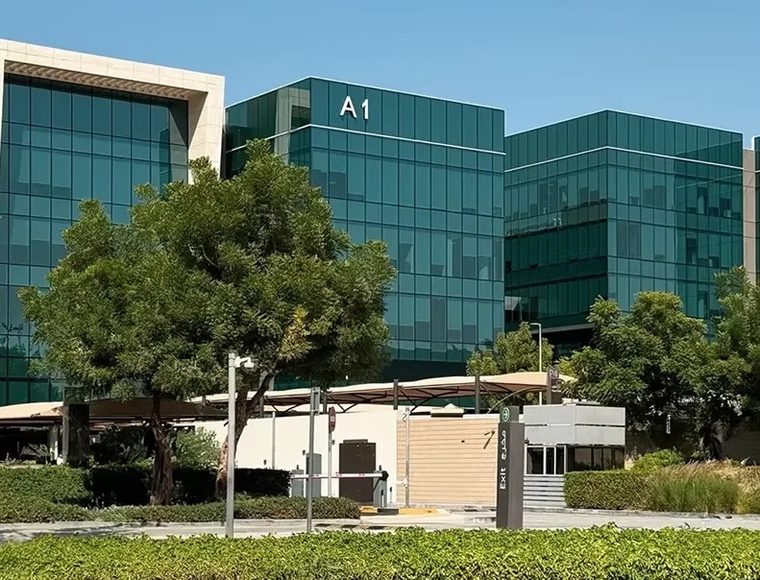
  • The Spirity office in Dubai

    Dubai

    Building A1, Dubai Digital Park

    Dubai Silicon OasisDubaiUnited Arab Emirates
    hello@spirity.ae
  • The Spirity office in Vienna

    Vienna

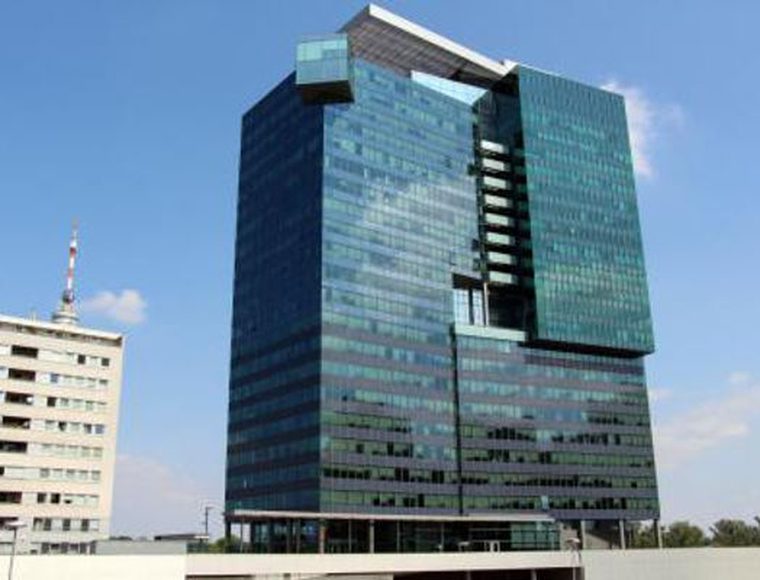
    Saturn Tower

    Leonard-Bernstein-Straße 10.Vienna, 1220Austria
    hello@spirity.at

Full registration and tax details for each entity are on the Impressum.

Credentials

Independently certified, independently verified

Our own house is in order. The standards we hold ourselves to are the ones we help our clients meet.

  • ISO/IEC 27001 system certification mark issued by SGS

    ISO/IEC 27001 Certified

    We are certified under the internationally recognized ISO/IEC 27001 standard for information security management.

  • UKAS Management Systems accreditation mark, number 0005

    UKAS Accredited Certification

    Our certification is accredited by UKAS, ensuring independent validation of our security and compliance practices.

  • Dun & Bradstreet AAA Highest Creditworthiness badge issued to Spirity Enterprise Zrt., with its D-U-N-S number

    AAA Highest Creditworthiness (2026)

    Awarded the AAA Highest Creditworthiness rating for 2026, we are ranked among the most financially stable companies.

Our people

What the team holds individually

The certifications above belong to the company and are independently audited. These belong to the people doing the work — held across the team rather than by any one person.

  • Information security and audit

    • ISO/IEC 27001 Lead Auditor
    • ISO/IEC 42001 Auditor
  • Privacy and data protection

    • CIPP/E
    • Europrivacy Auditor
    • Data Protection Officer (DPO)
  • Offensive and defensive security

    • Certified Ethical Hacker (CEH)
    • Certified Network Defense Architect (CNDA)
  • Incident response and continuity

    • ISO/IEC 27035 Incident Management
    • Business Continuity Manager

These organizations have already trusted us

Clients include Notino, MVM, Slovenská pošta, Audax Renewables, E.ON, Antenna Hungária, Lapker, Datacare, Delcap, FEAK, Fővárosi Vízművek, Gránit Bank, Grid Consulting, Hexagon, Insura, Merkantil Bank, Magyar Nemzeti Bank, Multi Alarm, NÜSZ, Magyar Közút, PortfoLife, Pharma Center, Teladoc Health, Sociálna poisťovňa, Austrian Red Cross, CREDEM Banca, Oando, MagNet Bank.
FAQ

Frequently asked questions

The questions we hear most often from security and IT leaders.

Something not covered here? Ask us directly

Spirity Enterprise is an independent, Hungarian-owned advisory firm working in IT transformation and cybersecurity. It was founded by IT and security leaders who came out of client-side careers in telecommunications, utilities and banking, bringing more than 25 years each of that experience with them — the company itself is younger than that number, and we would rather say so than let the two blur together.

We are deliberately small. The people who scope your work are the people who deliver it, which is a structural choice rather than a stage we are hoping to grow out of. It is also the main thing we are trading on: a firm this size cannot hide a weak team behind a brand.

Three registered entities: Spirity Enterprise cPlc. in Budapest, which is the head office, Spirity GmbH in Vienna, and Spirity Enterprise Middle East FZCO in Dubai. Each is a real company in its own register, with its own identifiers and its own contact address — the details are on our impressum page rather than implied.

Work can be delivered from any of the three. Which entity contracts with you is usually a question of where you are and what is convenient for your procurement, not a constraint on who does the work.

We work in Hungarian, English and German. On data: the answer depends on the service rather than on our address — the monitoring services keep your logs inside your own cloud tenant, and we say so on the pages where it matters. Ask us the question per service and you will get a straight answer; ask it of the company as a whole and any consultancy that answers confidently is guessing.

Both, split by layer, and we would rather show you the line than blur it.

Where we resell a partner platform — managed detection and response, supply chain monitoring, digital risk protection — we are the authorised reseller and your contracting party. That is not a formality: where a purchase is made through an authorised reseller, the terms agreed between the reseller and the client are the ones that govern. One contract, one accountable party, and escalation that comes to us rather than to a vendor support queue in another time zone.

Where the work is advisory, assessment, architecture, hardening, policy, programme leadership or a platform build, our own people do it. The evidence for that is the least glamorous thing we own: benchmark-measured hardening reports, firewall rule-base and network zoning proposals, SIEM deployments. Not slide decks.
Three things, which is what our own introduction deck has said for years: M&A advisory on the IT side, IT transformation, and cybersecurity — the last increasingly meaning compliance-driven programmes and virtual CISO work.

What we do not do, in order of how often it comes up. We do not run our own 24/7 security operations centre; that is our partner’s, under our contract, and pretending otherwise would be found out in one question. We do not certify anyone against ISO 27001 or CMMC — the accreditation rules bar a firm from certifying a management system it helped build, and we hold our own certificate rather than issuing anyone else’s. We do not touch your production systems on the advisory engagements: we specify, verify and write the evidence, and somebody with access makes the change.
And we are not an SAP application security practice, a penetration testing boutique, or the right answer for a company that wants a global follow-the-sun SOC as its prime contractor.

The same ones, because there are not enough of us for it to work any other way.

The engagements are staffed as named roles rather than a pool. On a compliance programme that is a lead advisor who owns the relationship and the reporting to your executives, a qualified security officer where the role is a statutory requirement, a consultant for the policies and evidence, and a technical expert for the access, endpoint, logging and backup controls. On a transformation programme it is a programme manager plus lead business and IT architects.

One deliberate structural point: the service is built so that it does not depend on one person being reachable. That is the failure mode of a part-time senior engagement, and the answer is a named team with defined roles rather than a single heroic consultant with a mobile number.

Telecommunications, energy and utilities, and banking and financial services. Those three are not a market-segment list; they are where the founders spent their careers before this company existed, which is a different kind of knowledge from having done a project there.

The reference engagements behind that: one of the largest Hungarian banks with international subsidiaries, where a supply chain, brand protection and executive protection programme went on to be rolled out across eleven countries; a Hungarian telco’s greenfield security operations centre, including its preparation to sell that capability onward; an ICT group’s telco M&A programme, where we led the IT transitional service agreement negotiation; and an energy-sector merger, where the same methodology carried governance from the due diligence through to project closure.

We also work in automotive and the public sector, with less depth, and we will say which is which.

A fair question, and one most firms answer imprecisely.

Spirity holds ISO/IEC 27001, obtained in early 2025 through a UKAS-accredited certification body, scoped to our own operation as a managed security service provider. That certifies how we handle information — including yours, while we hold it. It is not a certificate for your organisation, and no supplier’s certificate ever is.

Our delivery team holds Microsoft Azure Security certifications, and on the compliance side our consultants carry the individual certifications you would expect for this work. We also hold a top-band creditworthiness rating, which matters less to a security reviewer and more to a procurement department.

If a certificate is load-bearing for your decision, ask us for the scope statement rather than the logo. That is the document that tells you what was actually assessed.

A Big Four engagement tends to give you a report. A large MSSP tends to give you a platform. Neither owns the middle, and the middle is where most security programmes stall — the part where the findings become somebody’s actual job.

What we offer against that: the people who scoped the work also deliver it; advisory and technical capability sit in the same team, so a roadmap is written by people who will have to build against it; and partner-grade platforms come through one contract with us rather than a separate relationship for each.

Where we are the wrong answer: if you need a certifying auditor, a global follow-the-sun SOC as your prime contractor, or the institutional cover of a brand name in front of a board that will not accept a smaller firm. Those are real reasons, and we would rather say them here than discover them in a procurement round.

Ready to work with us?

Tell us where you are and what is worrying you. We will tell you honestly whether we are the right people for it.