Free self-assessment · 40 minutes · Supply chain
You did not build it. You are still answerable for it.
Integrators, resellers, operators and service providers are being asked product-security questions they never expected to answer — by customers, by insurers, and increasingly by the manufacturers themselves. This is seventeen questions about what you actually do with somebody else’s product.
Who it is for
You work with products with digital elements without placing them on the market yourself. You install them, resell them, run them for a client, or keep them working. The regulation lands on the manufacturer; the questionnaire lands on you.
What it covers — four areas
- Governance, documentation and risk (5)
- Awareness, competence and skills (5)
- Product life cycle management (4)
- Vulnerability and patch management (3)
It exists separately because the manufacturer’s assessment asks things you cannot answer — you did not design the product and you do not control its roadmap. What you do control is which versions you deploy, how quickly you patch what you operate, what you tell a customer when a vulnerability is published, and what happens when the manufacturer ends support.
What you get
A maturity level per area, adapted from the same ENISA model the manufacturer assessment uses — so if a manufacturer you work with has run theirs, the two reports speak the same language. The advice comes as a “Where you stand” page: what your level means in practice, then specific next steps under each of the four areas, written as the things a customer asking about your supply chain would want evidenced. Your answers are listed in full at the end.
There is no severity-ranked list of findings on this scale.
What the report looks like
Three pages from a real report, generated by running the assessment.
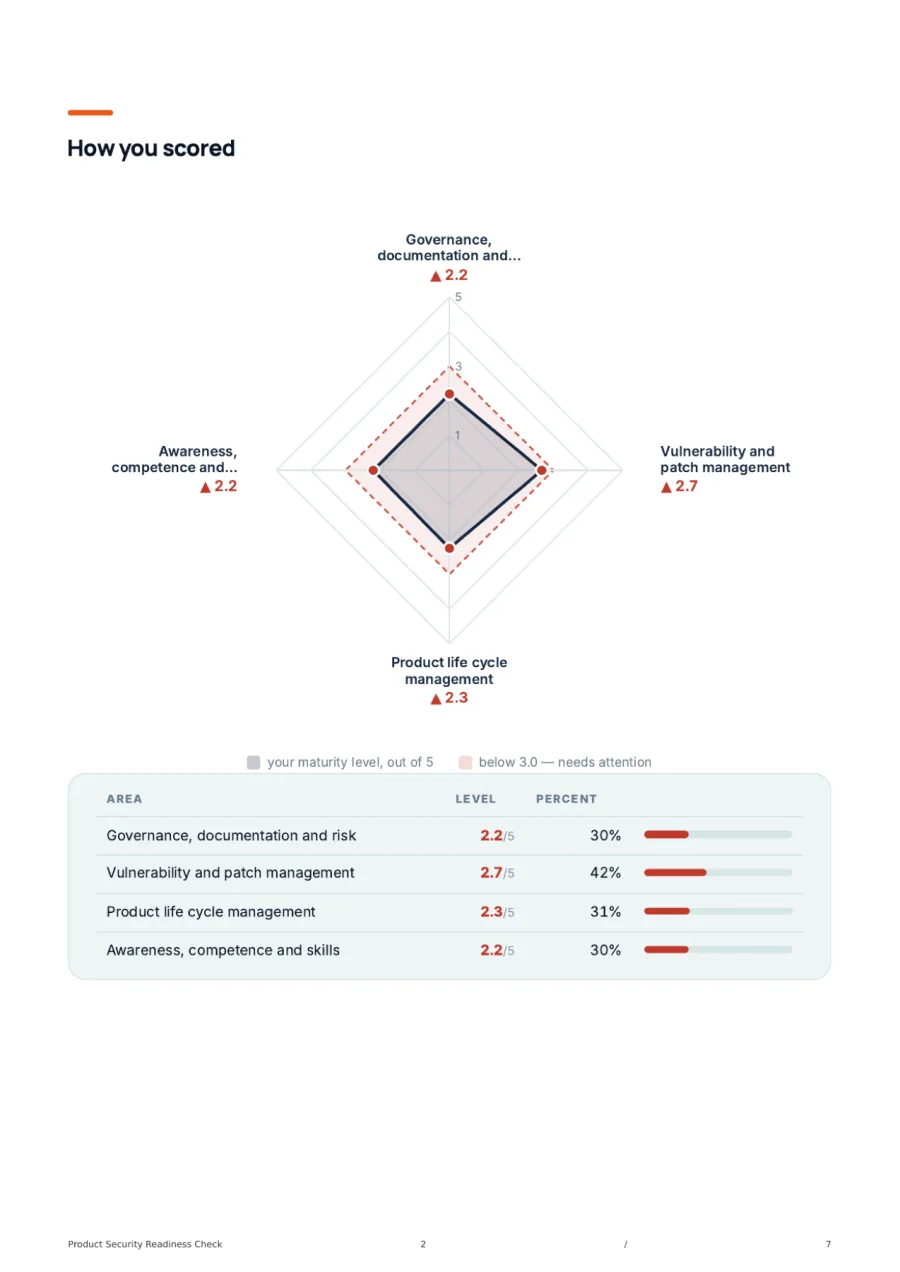
How you scored 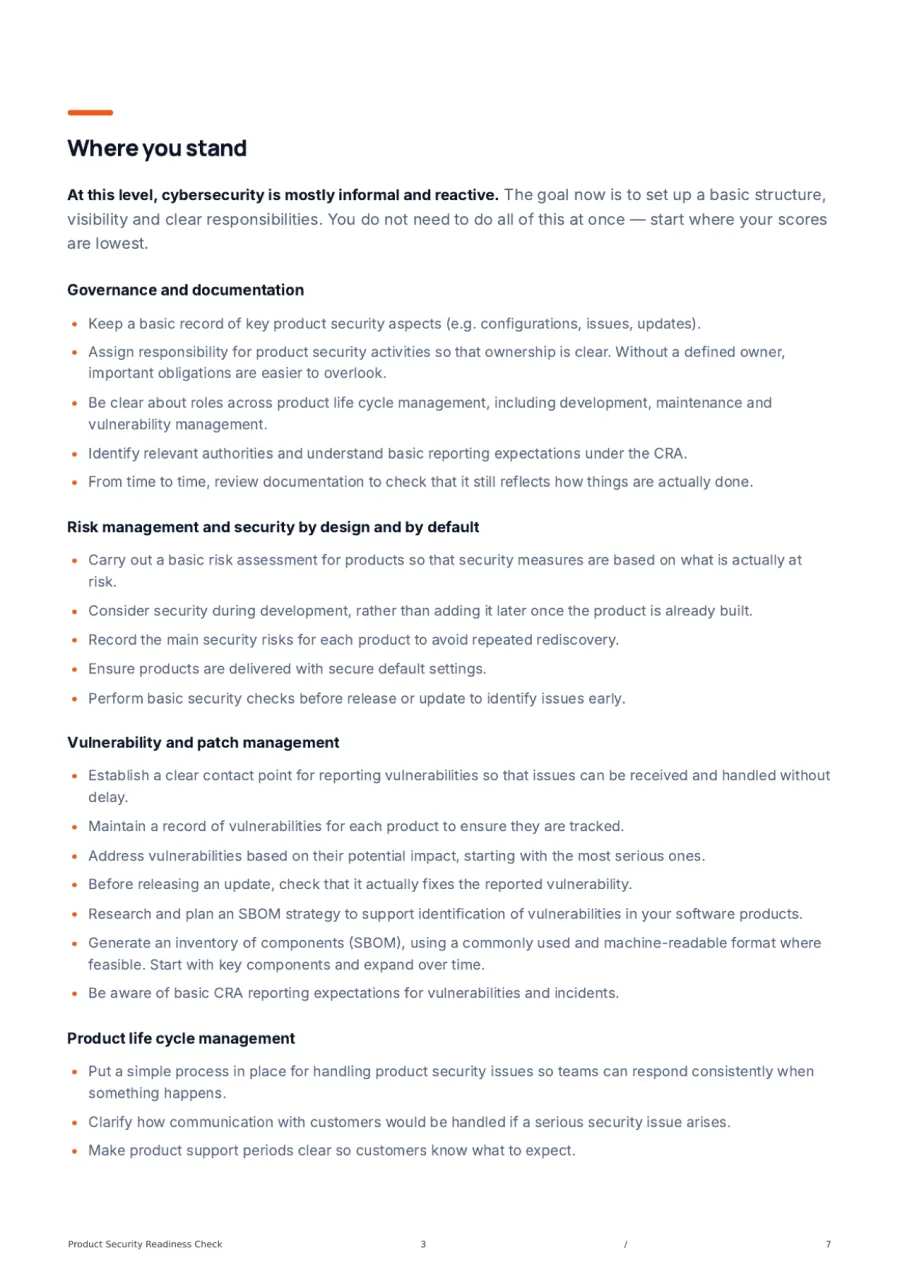
Where you stand 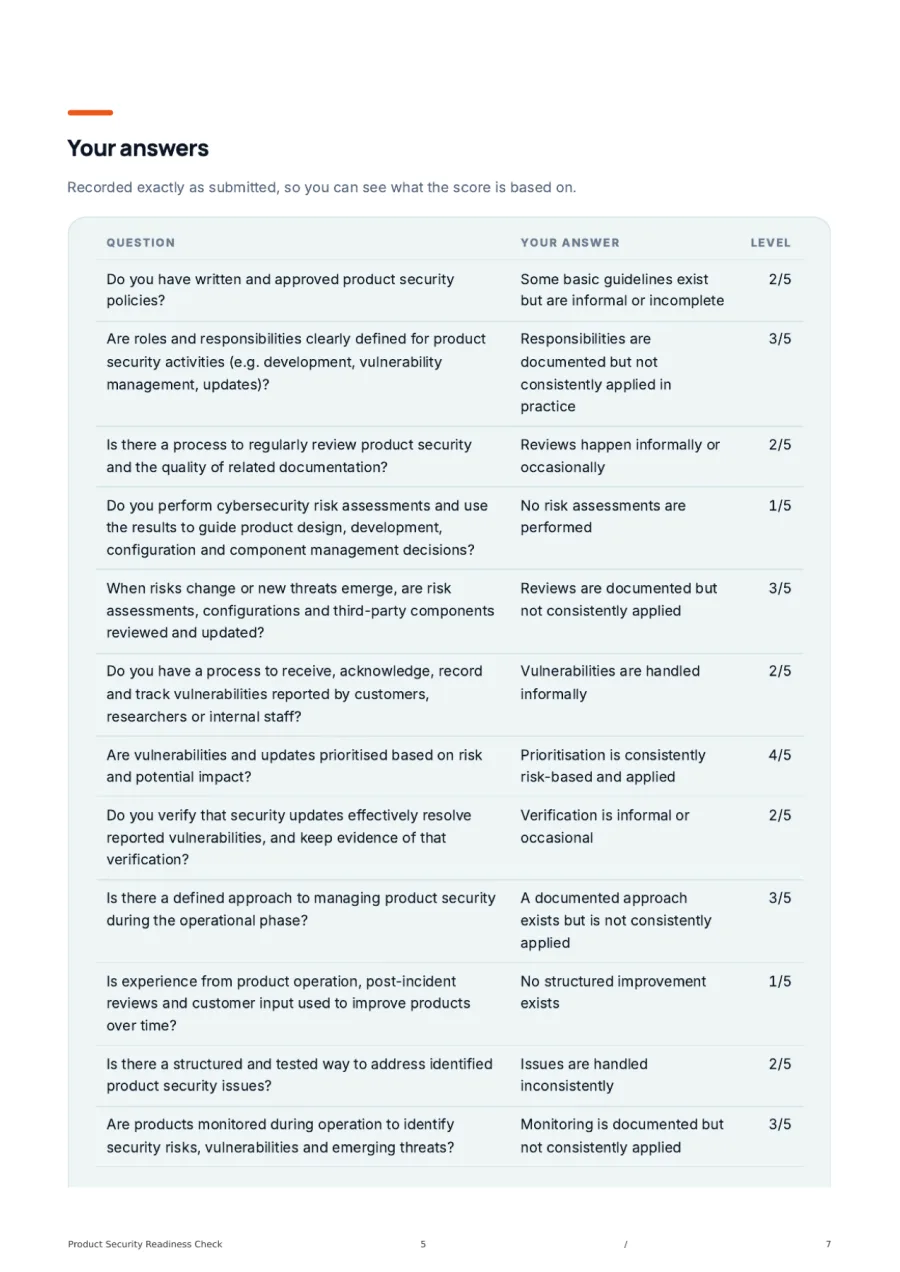
Your answers
The end-of-support question
The one most organisations have no answer to: what happens to a product you installed at a client when the manufacturer stops supporting it. It is worth knowing before a customer asks it in a renewal.
The assessment starts below — you do not need to go anywhere else.
A few details first
We use these to prepare your report and, if you would like, to talk it through afterwards.
Frequently asked questions
The questions we hear most often from security and IT leaders.
Something not covered here? Ask us directly
No, and it is deliberately shorter. That one measures a manufacturer against the regulation. This asks what you do with products somebody else manufactured — which versions you deploy, how fast you patch what you operate, and what you tell a customer when a vulnerability is published.
Usually yes. Reselling puts you in the chain your customer will ask about, and “we only resell” has stopped being an accepted answer to a supply-chain questionnaire. The seventeen questions are about what you control, which for a reseller is less than a manufacturer and more than nothing.
That is itself an answer, and worth recording. Several questions here are about what you can find out and what you do when you cannot — whether you know the support end date, whether there is a route for reporting a vulnerability, whether you have an alternative. A manufacturer who will not engage is a risk you carry on your customer's behalf.
The questions are plain and short, but they are in English, as is the report — there is no German or Hungarian version of the questionnaire yet. If that is awkward, answer it together with someone comfortable in English rather than guessing: a wrong answer here costs more than the extra half hour.
They are not quick questions. Most require checking what actually happens rather than what everyone assumes — whether patches reach the installed base, who is named for a vulnerability report, what the contract says about end of support. That checking is the part worth the time.
Ready to get started?
Partner with Spirity Enterprise to implement the right security and IT solutions for your organization.