General counsel are inheriting cyber ownership before boards name a single owner
Published October 7, 2026·5 min read
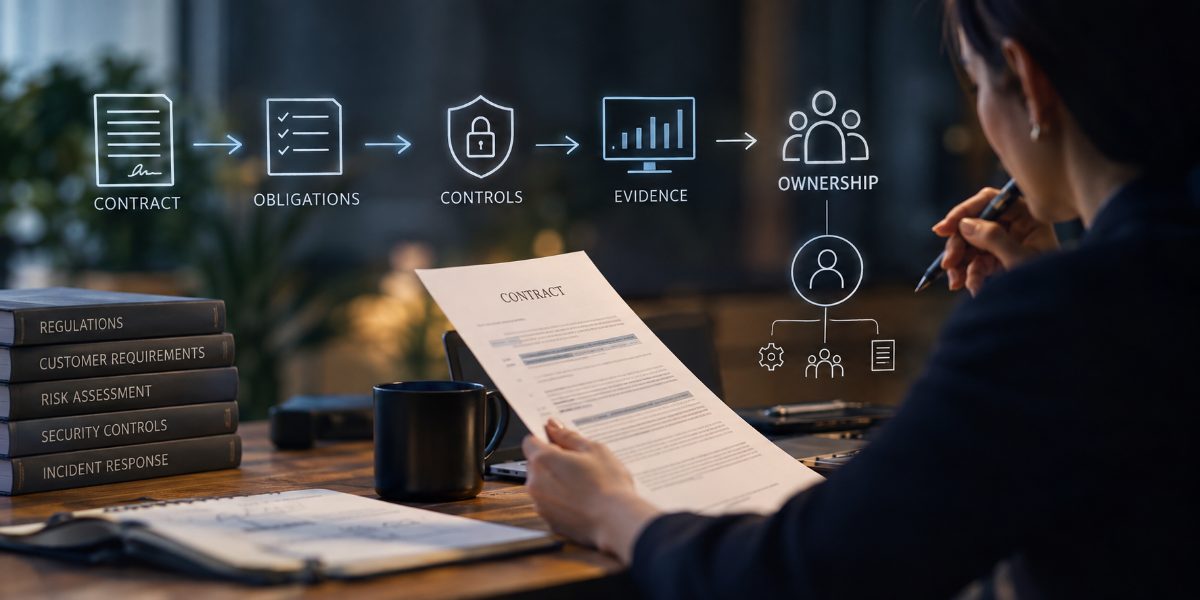
The question arrives on the general counsel's desk before it reaches the board: who in this organisation owns the security commitments we made in that contract, and can that person show it? By the time it is asked, it is a question about liability as much as technology. Lexology published a piece on 6 October 2026 under the title "What GCs say effective cyber leadership requires". The article sits behind a registration wall, so the visible substance is limited to a one-sentence framing: senior lawyers explaining how their function can improve board decisions, sharpen accountability and make incident plans work under pressure. The phrase that matters is "clarify ownership".
The easy reading is that general counsel are taking a bigger interest in cyber. That understates what is happening. Legal is being pulled into a conversation where ownership is already unresolved; in many organisations, legal becomes the owner by default, because nobody else can answer the question a regulator or a contract actually asks. A board may wait while the IT manager explains the firewall. A regulator asking which individual is accountable for risk decisions does not, and neither does a customer's security questionnaire that lands in the legal inbox before renewal.
Ownership fails before the technical controls do
For an organisation without a permanent security leader, ownership tends to be spread across the org chart. The IT manager owns the tools. The finance director owns the supplier contract. The operations director owns the data-entry process. The general counsel owns the liability. None of them owns the translation between a clause in a customer contract and a control in the environment. When a security questionnaire asks who is responsible for information security, the answer is often a name that makes the form go away, while the authority to change anything sits somewhere else.
The phrase "clarify ownership" is legal language for a control problem. A named owner must be able to do more than take the title. They need to know which obligations the organisation has accepted, which controls meet them, and what evidence exists when the question is asked again. For a company of a few hundred people, that is rarely a full-time role, but it is a real one. It is the role a virtual CISO fills: a named person who carries security ownership through the risk assessment, the remediation plan, the compliance evidence and the reporting line to leadership.
The translation between the clause and the control
The general counsel can name the duties. They are the person in the room who knows what a data processing clause says, what a sector rule expects, and what a board resolution has promised. The difficulty is that those duties are usually expressed in language that a firewall cannot satisfy. A clause requiring appropriate technical and organisational measures is a legal conclusion, not an implementation instruction. Somewhere between the contract and the environment, that language has to become a decision about multi-factor authentication, patching cadence or who may approve access. That translation is where ownership breaks down.
A person who can hold both sides is the missing piece. Legal advice stops where the contract ends. Technical work starts at the firewall. The space between them is where the finding lands after an incident, and where regulators aim their questions. A security owner's job is to be answerable across that space. For organisations that have not hired a full-time CISO, that person still needs to exist. They do not have to be an employee to be accountable, but they do need a mandate and a line to the board.
The question that changes the board paper
The board paper on cyber risk is usually a list of projects: items completed, items planned, budget requested. Before the next one is approved, the general counsel can ask a single question. For every commitment the organisation has already made — to a customer, a regulator or a standard — who is the named owner today, and what evidence can they show this quarter? If the answer is a committee, the organisation has no owner. If the answer is a person with no access to the risk register, the name is on the form and not in the decision.
The remedy is not necessarily to recruit a chief information security officer next month. At a few hundred seats, that hire is seldom the first step. The first step is to engage someone who can act as the single point of accountability: assess current state against the obligations, map them to framework requirements, set out a plan leadership can approve, and produce a report the general counsel can rely on in the next contract negotiation or regulator conversation. The role can be part-time or external. What matters is that the name on the organisation's answer is the same name in the board minutes and the incident plan.
If the gap is suspected but unmeasured, a short scored self-assessment is a low-cost way to see where the organisation stands before the next board paper arrives. It will not close the gap. It will show how wide it is, and who needs to own it.
A general counsel's accountability will keep growing as contracts and regulators name individuals rather than departments. Organisations that answer cleanly will be those where the legal owner and the technical owner are one named person, supported by evidence. For everyone else, the next questionnaire will simply ask the question earlier.
- cyber governance
- general counsel
- security ownership
- virtual ciso
- board reporting
- incident planning