The EDPB has just published the five questions behind every GDPR fine
Published October 1, 2026·4 min read
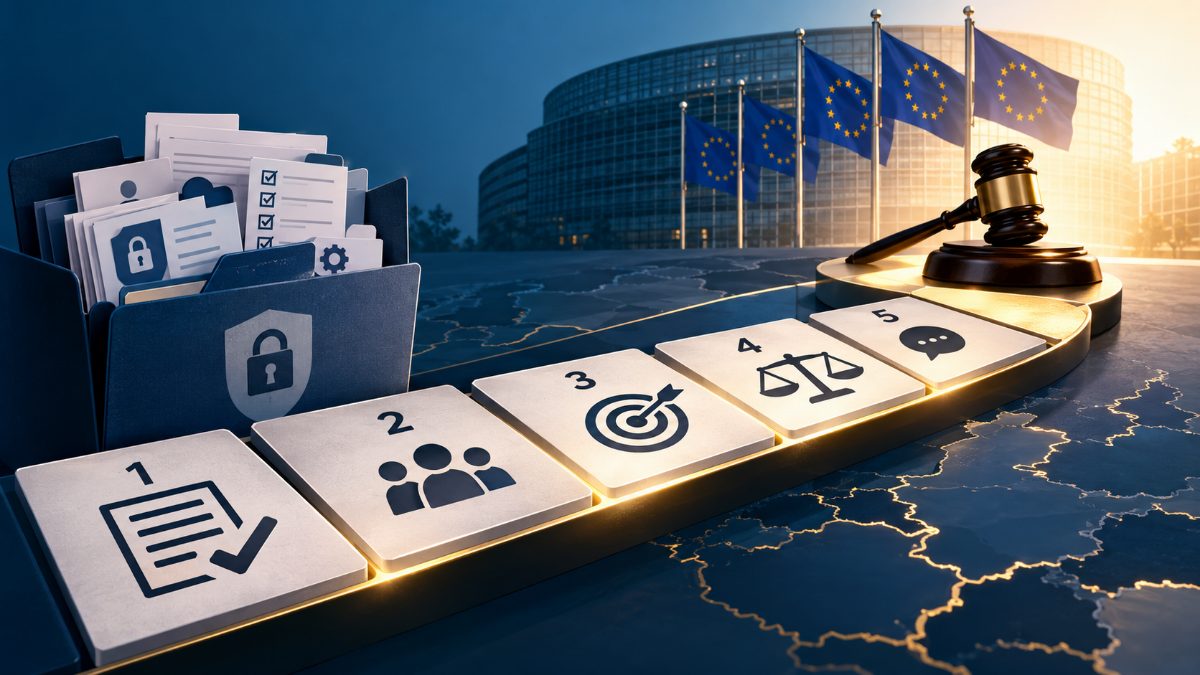
Ask anyone who has sat across from a supervisory authority what a GDPR fine ultimately turns on, and the honest answer is usually: which authority, which investigator, and how well the incident log was kept. Some of that variation is meant to reduce. On 25 September the European Data Protection Board opened a consultation on draft guidelines that set out a five-step methodology for deciding whether a fine should be imposed, reported by Pinsent Masons. The consultation is open until 13 November.
The draft does not introduce new fine levels. It works on the question that comes earlier: should there be a fine at all? Regulators are walked through five questions in sequence. Does the infringement fall within the category that can attract a fine? Can the party under investigation be held liable? Was the conduct intentional or negligent? What aggravating and mitigating factors under Article 83(2) apply? And is the matter minor enough that a reprimand is the more appropriate tool than a financial penalty?
The natural reaction misses the useful part
Most people will read this as enforcement news and wait for the final text. That would waste the lead time. The questions that determine exposure are mostly knowable in advance, from evidence the organisation should already hold. Whether an infringement can attract a fine is a property of the processing activity, not of the incident. Whether the party can be held liable is visible in contracts, instructions and decision rights. Whether conduct was intentional or negligent turns on policies, training, risk assessments and what management did after warnings. The aggravating and mitigating factors turn on the actions the organisation took.
Security teams already hold most of this in fragments. Training completion rates sit in the LMS. Processor instructions live in supplier contracts renewed on a calendar, not reviewed against exposure. Risk assessments are signed and shelved. The value of the methodology is that it names the order in which a regulator will read those fragments.
The culpability point deserves more attention than it will get. The draft states that an infringement must have been committed intentionally or negligently before a financial penalty can be imposed, and makes clear that Article 83 does not permit administrative fines in the absence of wrongful conduct. The EDPB calls a "culpable infringement" an unwritten but necessary condition of a fine. This is the distinction between a regulator deciding to fine and a data subject claiming compensation: compensation requires infringement plus damage, while a fine requires intent or negligence. None of this is binding while the text remains in consultation, and enforcement will always depend on the authority and the facts. But the direction is legible enough to prepare against.
Processor instructions become the deciding field
One paragraph will interest anyone whose customer data sits in a SaaS platform or an outsourced processor. Paragraph 42 starts from a default: the controller remains answerable for infringements a processor commits while acting on the controller's behalf. The processor only carries its own exposure when it ignores the controller's instructions, uses the data for its own ends, or otherwise leaves the agreed processing framework. When that happens, the processor may become a separate controller under Article 28(10) GDPR and bear responsibility for the processing.
In operational terms, the question is whether the instructions inside a data processing agreement are specific enough that a regulator can see where the controller's authority ended and the processor's own decisions began. If a breach happens because the processor did something the agreement neither authorised nor expressly forbade, the argument becomes about the gaps rather than the boundaries. For many mid-market organisations, those instructions were written by the supplier's legal team during procurement and are never read again. Pull the last three DPAs and read them as exposure documents, not as procurement artefacts.
A question for the board
If you are the person who answers for GDPR at board level, the consultation gives you a way to make exposure concrete without waiting for a breach. Board papers often describe data protection as a status word. The five-step methodology lets you ask a narrower question: for each material processing activity, can the organisation show at the moment a regulator asks that the conduct was neither intentional nor negligent, and can it evidence the mitigating factors it would rely on?
The deliverable is a fine exposure file. For each major processing activity it should hold the risk assessment, the training record for the people who control it, the processor instructions and their last review date, and the incident history that shows what was fixed and how quickly. This is not a compliance report; it is the file a regulator will expect to be shown in the first weeks after a breach.
The consultation closes on 13 November. Anyone who wants to shape the final methodology should respond. Anyone who wants to be ready for it can start the file now. We run this kind of structured gap review as part of our cybersecurity advisory and governance work, and where ownership is the problem rather than content, an interim security leader through virtual CISO services can hold the workstream without waiting for a full-time hire.
The dials are visible now. The question is whether your folder would hold up if someone turned them.
- gdpr
- data protection
- governance
- regulatory enforcement
- third-party risk
- cybersecurity advisory