The EBA just made internal control vendors critical by default
Published October 20, 2026·4 min read
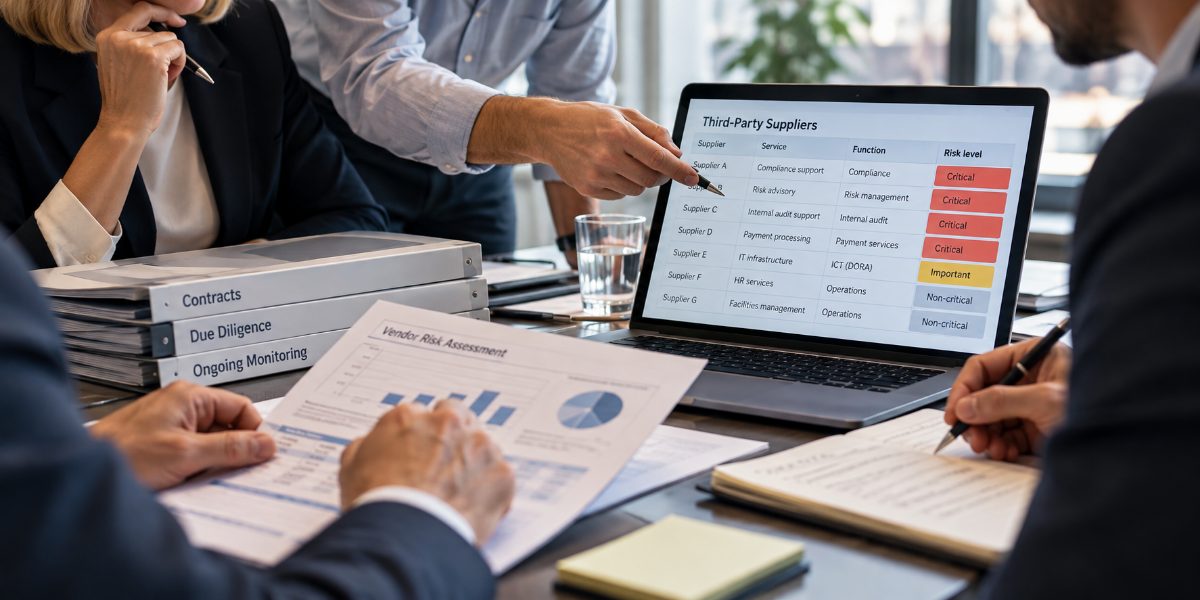
A risk officer at a payment institution arrives at the board with a tidy register. Six suppliers are marked critical. The compliance function's outsourced monitoring support sits in the "non-critical" tab. Under the EBA's final guidelines, that slide is wrong before it is shown.
Deloitte reported on 25 September 2026 that the European Banking Authority published its final Guidelines on the sound management of third-party risk regarding non-ICT services on 18 September (EBA/GL/2026/09). They replace the 2019 outsourcing guidelines. Much of the industry will read them as a contract renegotiation project. The more urgent change is to who gets called critical, and who has to prove otherwise.
The presumptions do the reclassification for you
The Guidelines now govern any "third-party arrangement" — an outside provider, including group companies, supporting a function on a recurrent or ongoing basis. That alone means an outsourcing register is no longer enough. The register is the record of one defined category; the Guidelines ask for a map of the whole vendor population.
Then two presumptions narrow the room to call something non-critical. A provider used for operational tasks of internal control functions — compliance, risk management or internal audit — is critical or important by default. A firm can rebut that only with an assessment showing a failure or inappropriate provision would not harm the effectiveness of those controls. A provider used for banking activities, payment services or asset-referenced token issuance to an extent requiring authorisation or registration is critical automatically, with no exception.
The result is that reclassification is not something your team decides at the next review. Some vendors move categories because the rule says so. For an institution where one person or a small team owns several hundred supplier relationships, the first step is not reading contracts again; it is rebuilding the inventory so the board no longer sees a self-assessed risk rating that has been overtaken by regulation.
Evidence has to outlive the signature
The contract changes matter, but they are downstream of the classification. Every arrangement now needs a baseline set of protections, including service location, governing law, data protection provisions, service level descriptions, termination rights and a duty to cooperate with competent and resolution authorities. Critical arrangements add detailed service level targets, audit and access rights, business contingency testing and an exit strategy with a transition period.
A completed questionnaire does not meet that. It records promises at the point of signature. Audit rights have to be executable. Contingency testing has to be scheduled. Exit strategies have to work under stress. That is what shifts the work from procurement-time assurance to ongoing evidence, and it is where a firm without a dedicated vendor assurance team hits a practical wall. A managed programme that runs continuous supplier monitoring and remediation changes the question from "did they answer the form" to whether the control can be shown to be true this quarter.
Don't let the DORA boundary confuse the picture
The EBA guidelines apply to non-ICT services. ICT remains under DORA, and not everything sold as an IT service belongs there. Bundled contracts have to be split between the two regimes; incidental ICT use requires a documented assessment of whether the ICT element is material enough to pull the whole arrangement under DORA. That boundary is itself a deliverable: a classification methodology procurement and security can apply without calling outside counsel on every deal. Framework mapping that separates EBA, DORA and national regimes is more useful than another generic compliance deck.
Exactly how the Guidelines sit alongside domestic outsourcing law depends on the member state. The source points to Sweden's separate Finansinspektionen regime, and other jurisdictions add their own parallel duties. That is a reason to build the map once and reuse it, rather than wait for a consolidated standard.
The danger in a mixed service organisation is that the DORA boundary becomes an excuse to postpone everything. The EBA side is where the new reclassification presumptions live. Delay there, and the two-year clock for critical arrangements is already running.
A question for the board
The board should ask for the list of suppliers reclassified under the final guidelines, and the documented evidence for any internal control supplier that was left non-critical. If the answer is a register last updated at contract renewal, the transition clock is already running. Critical arrangements have two years from the application date — still unconfirmed — for review and documentation, after which institutions must notify the competent authority with remediation plans or an exit strategy. Two years sounds like room until renegotiation lead times collide across a dozen large vendors at once.
The first task this quarter is to map the full vendor population against the new scope and the two presumptions, mark the internal control and regulated activity suppliers, and put the gaps in front of the board as something to be closed rather than discussed. The contract fixes follow. They always do.
- third-party risk
- eba guidelines
- vendor management
- board reporting
- dora
- supplier assurance