Does your payment approval process survive a live video call?
Published October 26, 2026·4 min read
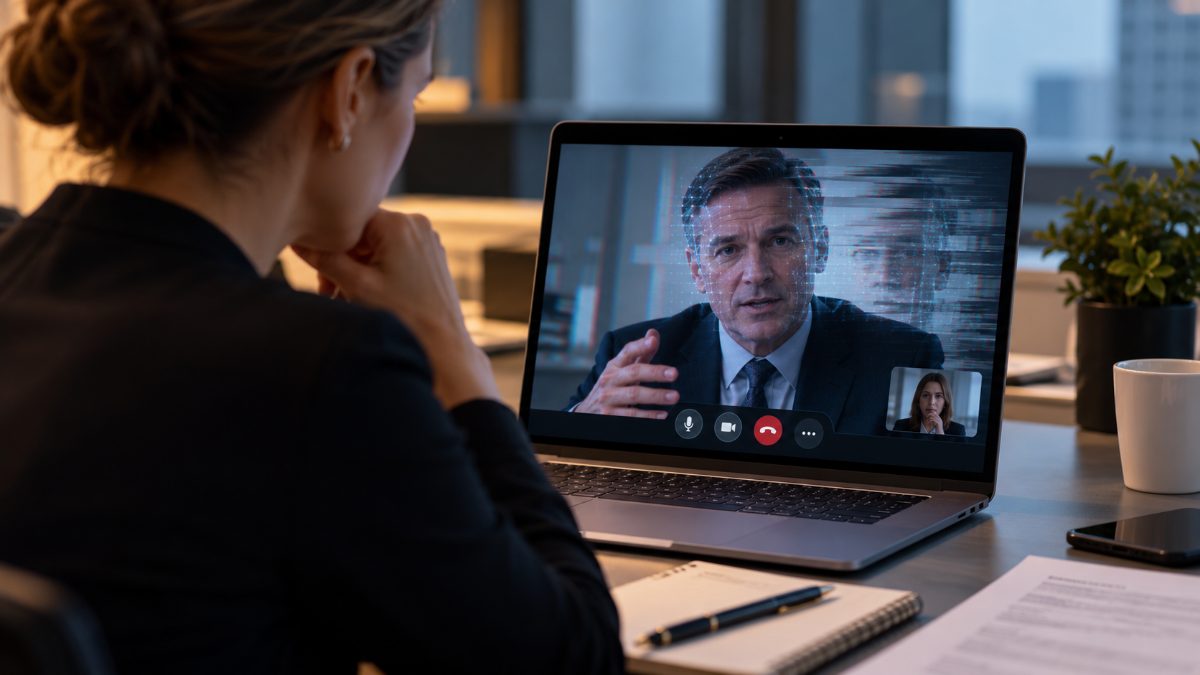
A finance worker transferred $25.6M across 15 transactions after a live video call in which the chief financial officer was a real-time deepfake. That case appears in a report identifAI published and Security Boulevard covered on 13 October, which puts AI-driven deepfake fraud at $40 billion and identifies video synthesis as the largest single method at 42.7 per cent, followed by voice cloning at 21.9 per cent.
The number will pull the conversation toward AI detection. That is the vendor-shaped conclusion, and for a mid-market organisation it leads toward a technology procurement with no end. The more useful reading is that the attack has moved from the inbox to live channels, and most payment approvals were written for the inbox. The useful change is independent verification rather than better pattern recognition.
Start with the raw material. identifAI reports that attackers harvest high-fidelity video and audio from public appearances, podcasts, interviews and social media, with X and LinkedIn among the main sources. For a visible executive, the voice and face your employees trust are already available to anyone. That is what makes the live call different: it carries the same familiarity signals a phishing email lacks, and it works against staff who have only ever been drilled to inspect URLs and sender addresses.
In practice, the vulnerable moment sits inside a finance team, away from any security operations centre. A supplier's bank details change, or an urgent payment must go out before a deadline. The person holding the keyboard knows the caller, has spoken to them before, and has no routine for saying I'll call you back on a number I already hold. If the call is a deepfake, the absence of that routine is the entire attack.
The second channel
The control that closes this is out-of-band verification. No payment detail change, executive transfer request, or sensitive data handoff should be completed on the strength of the channel that carried it. The confirmation has to come through a second, separately initiated route.
That can mean calling the requester on a number that already exists in your ERP or HR system, rather than a number or link supplied in the request. It can mean a second approver in another team confirming the instruction by phone or in person. For very large transfers, it can mean a short-lived code from a separate authentication app. The property that matters is that the employee does not decide in the moment whether the caller seems genuine. The process decides.
This is where security awareness actually pays for itself. A managed cyber awareness programme can assign the finance, HR and executive assistant teams role-specific modules that walk through exactly this scenario, then test it with simulated requests. The goal is a rehearsed, blame-free refusal. If an employee pauses a transfer and the caller turns out to be the real CFO, the outcome should be a small delay and a thanks. If the pause is punished, the next refusal will not happen.
Rehearse the refusal
The simulation matters more than the policy. A written rule that tells staff to verify urgent requests is not much use at 4 p.m. on a Friday, when the face on the screen is familiar and the instruction is specific. Rehearsal changes the default.
For email-based lures, a report-phish button sends the suspicious message to the SOC; call-based attempts should follow the same escalation path, even if the evidence is only a name and a number. A managed programme gives the loop structure: role-based modules, realistic simulated requests, and dashboards that show whether finance has actually completed the verification. Measure whether the check happened. The quiz score is beside the point. That is how you find the one team that still needs a revised procedure.
The board question
The question now in front of a board or finance director is straightforward: can your payment processes complete a supplier change or transfer on a single live request? Ask finance to walk through the last urgent payment change. How many steps were there? Which one would have stopped a synthetic CFO? If the answer is the person on the call seemed to know too much, then there is no control.
The source leaves a lot untested. The $40 billion figure is identifAI's tally, reported without methodology, and the Hong Kong case is not independently confirmed in the piece. But you do not need the full number to find the mechanism credible. It is already possible, and it is getting cheaper. The question is whether your approval process survives the day it is used on you.
- deepfake fraud
- payment fraud
- cyber awareness
- out-of-band verification
- executive impersonation
- social engineering