Austria's NISG 2026 goes live on 1 October — the managing director's deadlines land first
Published September 28, 2026·5 min read
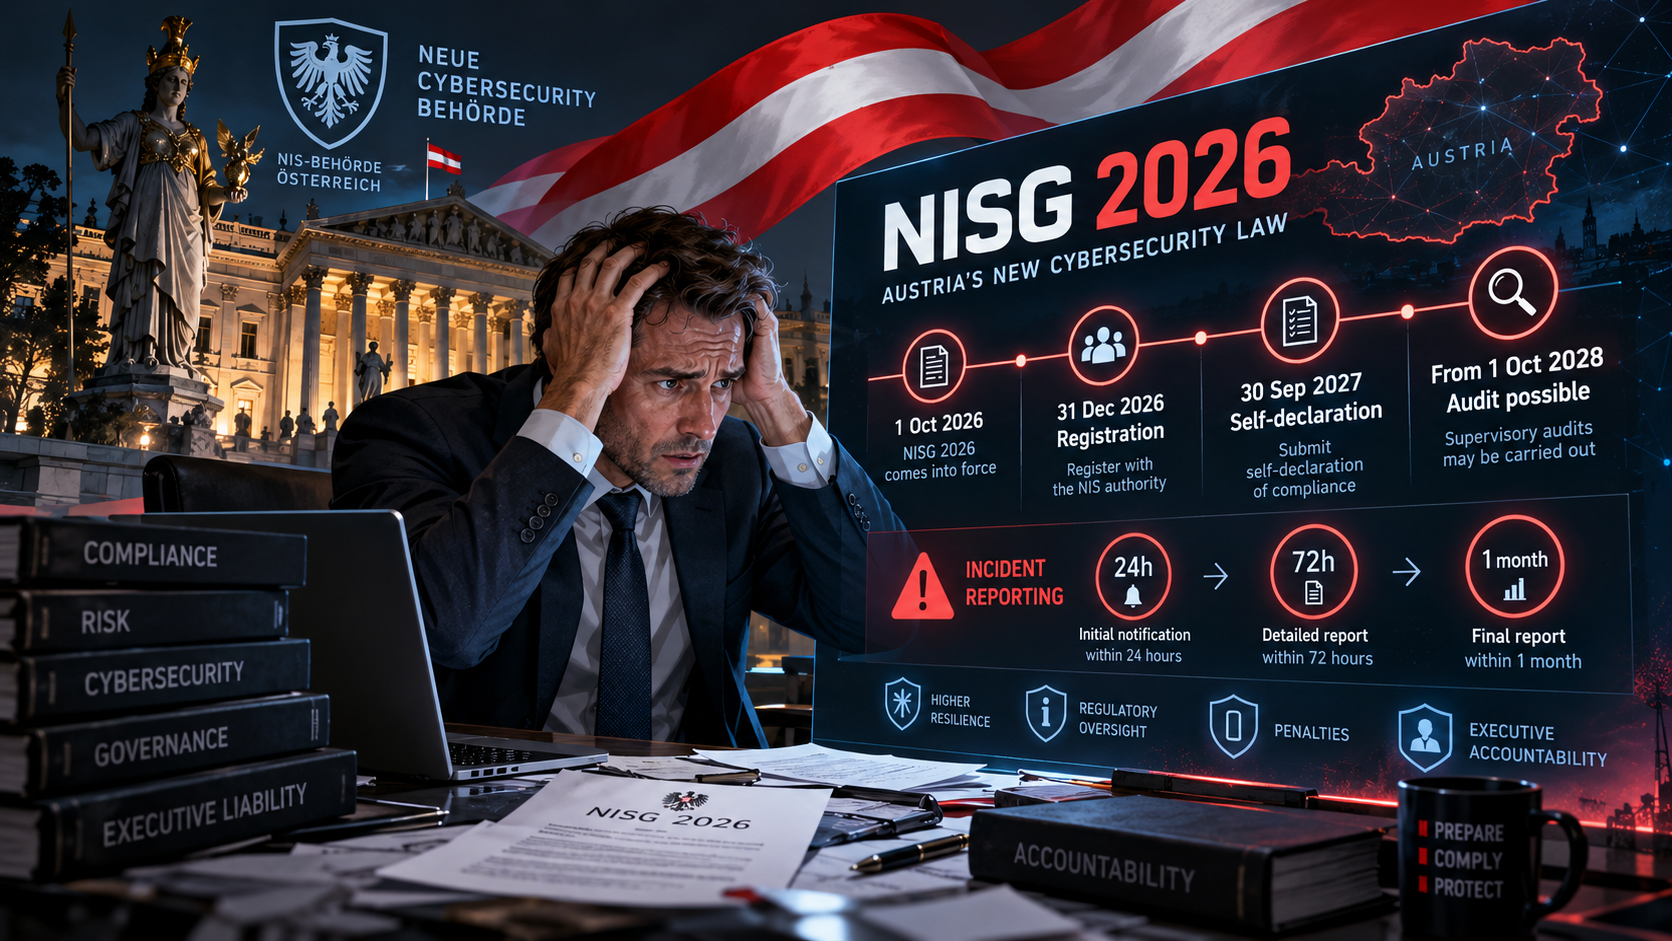
On 1 October 2026 the Netz- und Informationssystemsicherheitsgesetz 2026 (NISG 2026) enters into force and Austria's new Federal Office for Cybersecurity (Bundesamt für Cybersicherheit, BCS) starts work. The Austrian Federal Economic Chamber (WKO), in guidance updated on 24 September, puts the reach at around 4,000 organisations across 18 sectors — against roughly 100 under the NISG 2018 it replaces. That scale is the headline. The thing to act on is sharper: the law does not wait for implementation projects before its reporting and supervisory powers switch on.
What is live on 1 October, and what is not
From 1 October the NISG 2018 ceases to apply. Risk management measures and incident reporting duties run from that day, and the BCS can begin supervisory and enforcement action. That means an entity already in scope has no transition window for incident handling: a significant cybersecurity incident that becomes known after 1 October triggers a three-stage reporting chain to the responsible CSIRT — an early warning within 24 hours, a fuller notification within 72 hours, and a final report within one month. The first deadline you could miss is therefore not a filing date; it is the 24-hour clock that starts on the first serious incident.
Registration is the first administrative date: affected essential and important entities must register by 31 December 2026. The exact registration channel is still to be set by ordinance, but the deadline itself is fixed. A self-declaration on implemented risk management measures follows on 30 September 2027. The WKO's own page carries both that date and 1 October 2027 in different places; the Schönherr legal briefing uses 30 September. Whichever is confirmed, the work belongs in the first half of 2027, not at the year-end.
What can genuinely wait: an independent audit of the technical implementation can only be demanded at the earliest from 1 October 2028, and for important entities only where there are grounded indications of a breach. That is not a reason to delay the measures themselves — they are expected from day one. For non-digital sectors the detailed technical measures still await a national ordinance; the WKO recommends using the EU implementing act annex and its guidelines as the working reference in the meantime.
The managing director's deadline is personal before it is technical
Section 31 of the NISG 2026 addresses the management body directly. Managing directors and board members must approve the required risk management measures, steer their implementation and supervise them on an ongoing basis. Delegation to IT, information security or compliance does not move the responsibility. The same section requires participation in cybersecurity training designed for executives — a general IT induction is not enough.
This is the part many compliance calendars underweight. The fines sit with the entity — up to €10 million or 2% of global turnover for essential entities, €7 million or 1.4% for important ones, and up to €50,000 for a missed registration, or €100,000 for repeat organisational breaches. But the personal exposure sits in company law: if a director breaches the duty of care and the company suffers damage, they can be liable internally. For essential entities the BCS can also prohibit a director from exercising their function and require an entry in the company register. The training obligation is therefore not bureaucratic; the Schönherr briefing describes it as liability protection, which matches how a supervising board should treat it.
Where most readers will feel it first
The direct scope applies to medium and large organisations in 18 sectors: medium means at least 50 employees or more than €10 million turnover with balance-sheet total above €10 million; large means at least 250 employees or more than €50 million turnover with balance-sheet total above €43 million. Certain providers are caught regardless of size — trust service providers, public electronic communications networks and services, TLD registries and DNS providers among them.
But the practical reach is wider. In-scope entities must secure their supply chain and can pass contractual risk-management obligations to direct suppliers. A company below the thresholds can therefore still receive a demanding security questionnaire as a condition of keeping a customer. The BCS also has the right to conduct active scans of internet-facing systems of essential entities, and blocking those scans becomes an offence from 1 October. If you manage infrastructure, that is a technical change to plan for now.
For organisations that are not sure whether they are in scope, the first useful step is a genuine scope check. Our free NISG 2026 check answers the ordinary case in about fifteen questions and five minutes — anonymous, no registration, and the result appears immediately with the paragraphs it rests on. If the answer is yes, our NISG 2026 framework page sets out the full schedule: the four dates from 1 October 2026 to the possible audit from 2028, the five obligations behind them, and which detailed rules are already binding versus still waiting on a national ordinance. The registration page covers the 31 December deadline on its own, since that is the first date most in-scope entities will have to act on.
What to do this week
Confirm scope before the registration window closes. If you are in scope, put 31 December against a named owner, not a department. Book the management-specific training now; it is a statutory duty and the best documented defence you can create. Walk through the incident reporting chain with whoever would receive a 2 a.m. call, because the 24-hour early warning is already running. And if you supply in-scope entities, expect contractual security clauses to arrive; prepare a short, honest capability statement rather than reacting to each questionnaire from scratch.
If there is no internal security leader to run the gap assessment, prepare the self-declaration and give the board the supervision trail Section 31 expects, a virtual CISO engagement is the practical bridge between a compliance deadline and a functioning security programme.
The rules are summarised here for orientation; what applies to a specific organisation depends on its structure, sector and thresholds.
- nis2
- nisg-2026
- austria
- cybersecurity-compliance
- management-liability
- bcs